



Hello,
LDAP Users are added successfully to MC but can’t authenticate because MC is not overriding default search path at authentication. In the documentation, it is stated that an MC administrator can override the default LDAP search string if the user is found in another branch of the tree. In user management, I can verify and add a user belonging to a different branch from the one set in the Authentication parameters, however authentication fails because MC will use the search path specified in default search path.
Here is an example I run using an openLDAP Vertica 8.1, I have two users belonging to 2 different OU:
testldap ∈ OU= People,
dev1 ∈ OU=dev.
In the authentication parameters I set OU=People as Default search path: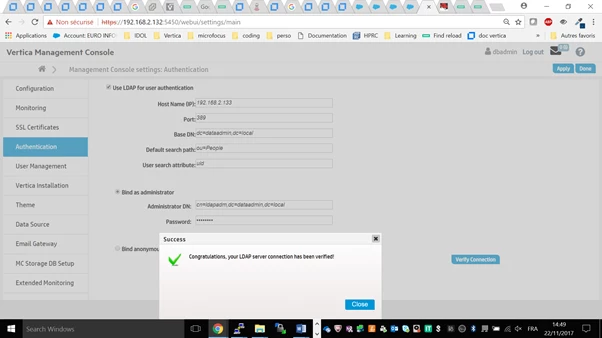
I can add the user testldap by keeping the default parameters, and in the openLDAP logs I have the following:
Nov 21 14:39:08 localhost slapd[1346]: conn=1299 op=1 SRCH base="ou=People,dc=dataadmin,dc=local" scope=2 deref=3 filter="(uid=testldap)"
To add the user dev1 I change the search path to OU=dev the verification returns true and the user is added correctly. So far so good, both users are added correctly. This is whet I have in openLDAP logs:
Nov 21 14:43:04 localhost slapd[1346]: conn=1313 op=1 SRCH base="ou=dev,dc=dataadmin,dc=local" scope=2 deref=3 filter="(cn=dev1)"
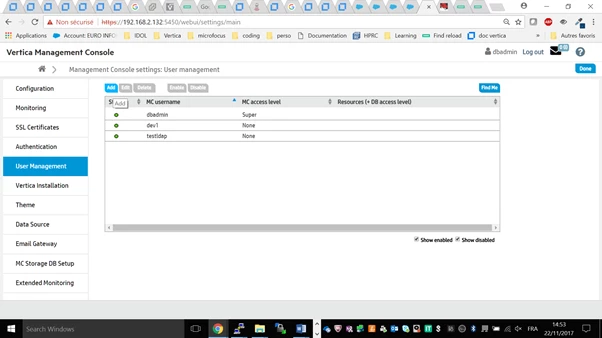
However I fail to authenticate using user dev1, and when I check the openLDAP logs, I find that the default search path was used to search for the user:
Nov 21 14:43:41 localhost slapd[1346]: conn=1314 op=1 SRCH base="ou=People,dc=dataadmin,dc=local" scope=2 deref=3 filter="(cn=dev1)"
Is this a known issue? Has anyone had this problem before?
Many thanks,
Chaima BERRACHDI



